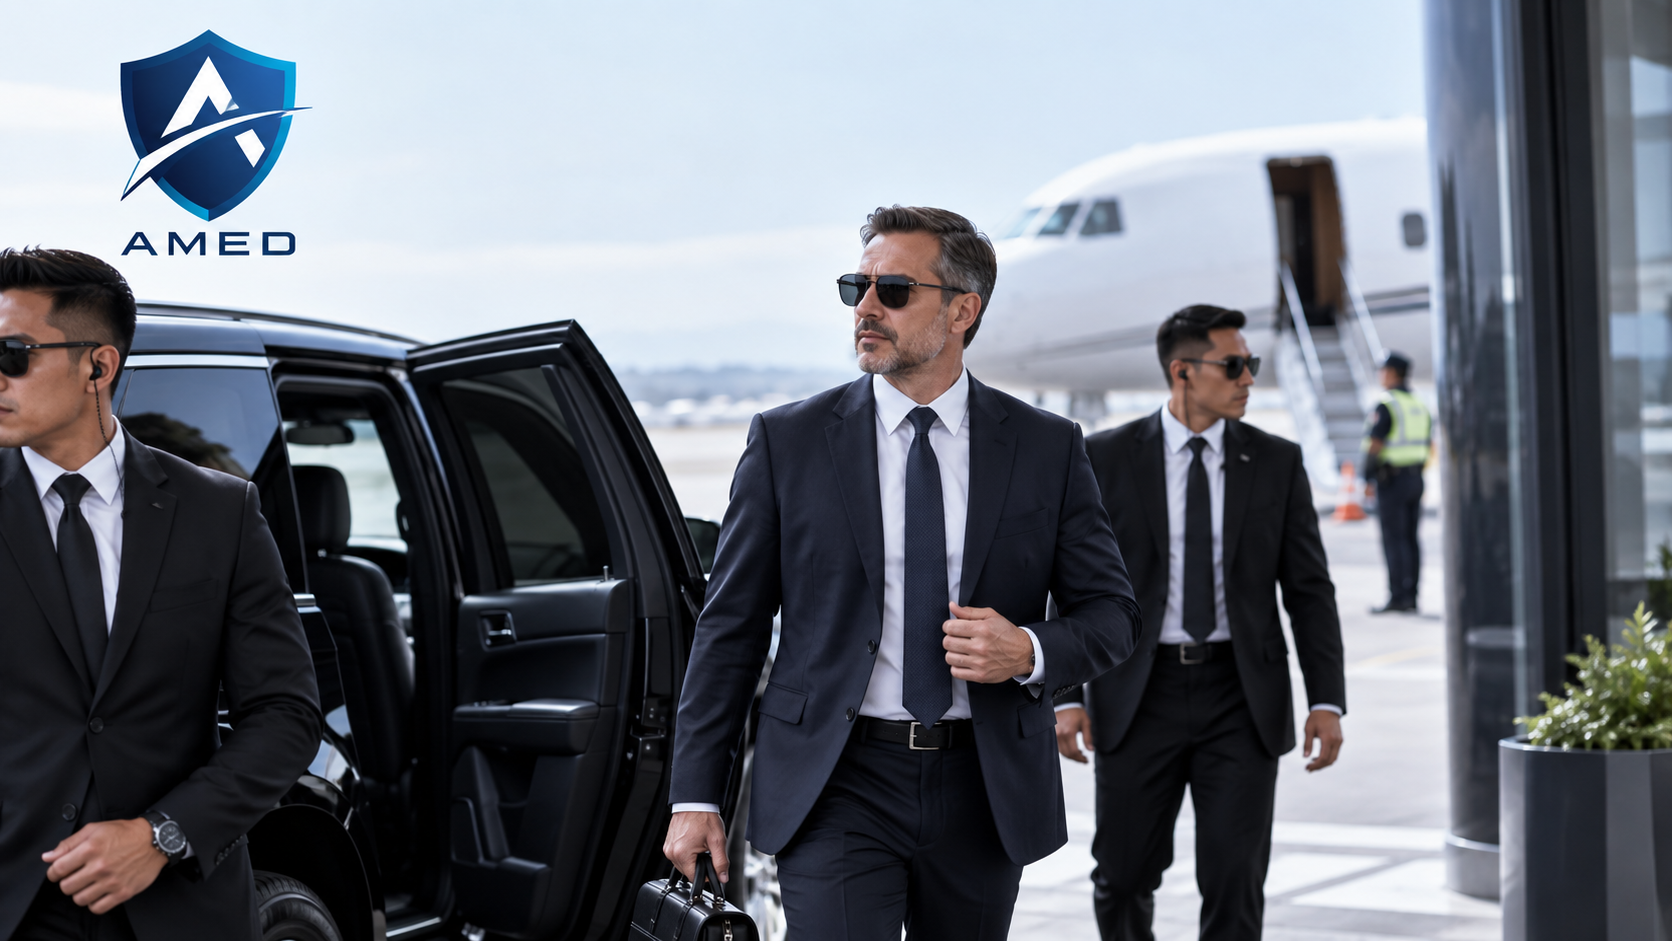
Cybersecurity executive protection is an integrated security approach that connects digital risk management with physical executive protection. For companies whose leaders handle confidential data, travel frequently, meet strategic partners, visit operational sites, or make high-value decisions, protecting the executive means protecting both the person and the information surrounding them.
An executive can have professional physical protection and still face risks through a compromised smartphone, phishing attack, stolen credentials, exposed travel itinerary, insecure Wi-Fi connection, or leaked meeting information. Conversely, strong cybersecurity controls alone cannot protect an executive from physical surveillance, unsafe transportation, unauthorized access, or security incidents during business travel.
For this reason, companies should stop treating cyber risk and physical security as completely separate disciplines.
The more effective approach connects:
Cybersecurity → Information Protection → Threat Intelligence → Travel Security → Secure Transportation → Executive Protection → Incident Response
This concept aligns with guidance from the U.S. Cybersecurity and Infrastructure Security Agency (CISA), which notes that cyber and physical assets can face separate or simultaneous attacks. CISA argues that organizations gain a more holistic view of threats when cybersecurity and physical security functions collaborate rather than operate in silos.
For executives operating or traveling in Indonesia, this integrated perspective becomes especially relevant because business activity often moves across airports, hotels, vehicles, offices, meetings, industrial facilities, and regional locations.
What Is Cybersecurity Executive Protection?
Cybersecurity executive protection combines cybersecurity awareness, information protection, physical security, travel risk management, secure transportation, threat assessment, and incident coordination to reduce risks surrounding executives and other key personnel.
Traditional executive protection primarily focuses on the physical safety of a principal. Meanwhile, cybersecurity focuses on digital assets, systems, identities, devices, networks, and information.
Modern executive risk does not always respect that distinction.
A leaked calendar can expose an executive’s location. A compromised email account may reveal confidential negotiations. Social engineering can target an executive assistant before a business trip. Meanwhile, information gathered through physical surveillance may help an attacker conduct a more convincing cyberattack.
Therefore, companies should think in terms of an executive risk ecosystem, rather than two independent security functions.
CISA describes security convergence as formal collaboration between previously separated security functions. According to its guidance, convergence supports integrated threat management, information sharing, strategic alignment, and common security goals.
Why Are Executives Both Cyber and Physical Security Targets?
Senior executives often have something ordinary employees do not: authority, access, information, visibility, and decision-making power.
A CEO may have access to strategic plans, financial information, acquisition discussions, investor communication, sensitive contracts, or confidential client information. Senior leaders can also authorize payments, approve transactions, influence employees, and access important systems.
Consequently, attackers do not always need to attack the corporate network directly. They may target the executive, family members, assistants, drivers, travel arrangements, personal devices, or people surrounding the principal.
From a cybersecurity perspective, risks can include phishing, credential theft, account takeover, impersonation, malicious links, device compromise, social engineering, data leakage, and insecure communications.
Physical risks can involve surveillance, unauthorized approach, unsafe routes, hostile environments, theft, travel disruption, or security incidents during meetings and site visits.
The critical point is the connection between them.
Digital Exposure → Intelligence Gathering → Executive Identification → Location Exposure → Physical Opportunity
The sequence can also move in the opposite direction:
Physical Observation → Information Collection → Social Engineering → Credential Attack → Corporate Access
That relationship explains why cybersecurity executive protection requires coordinated risk management.