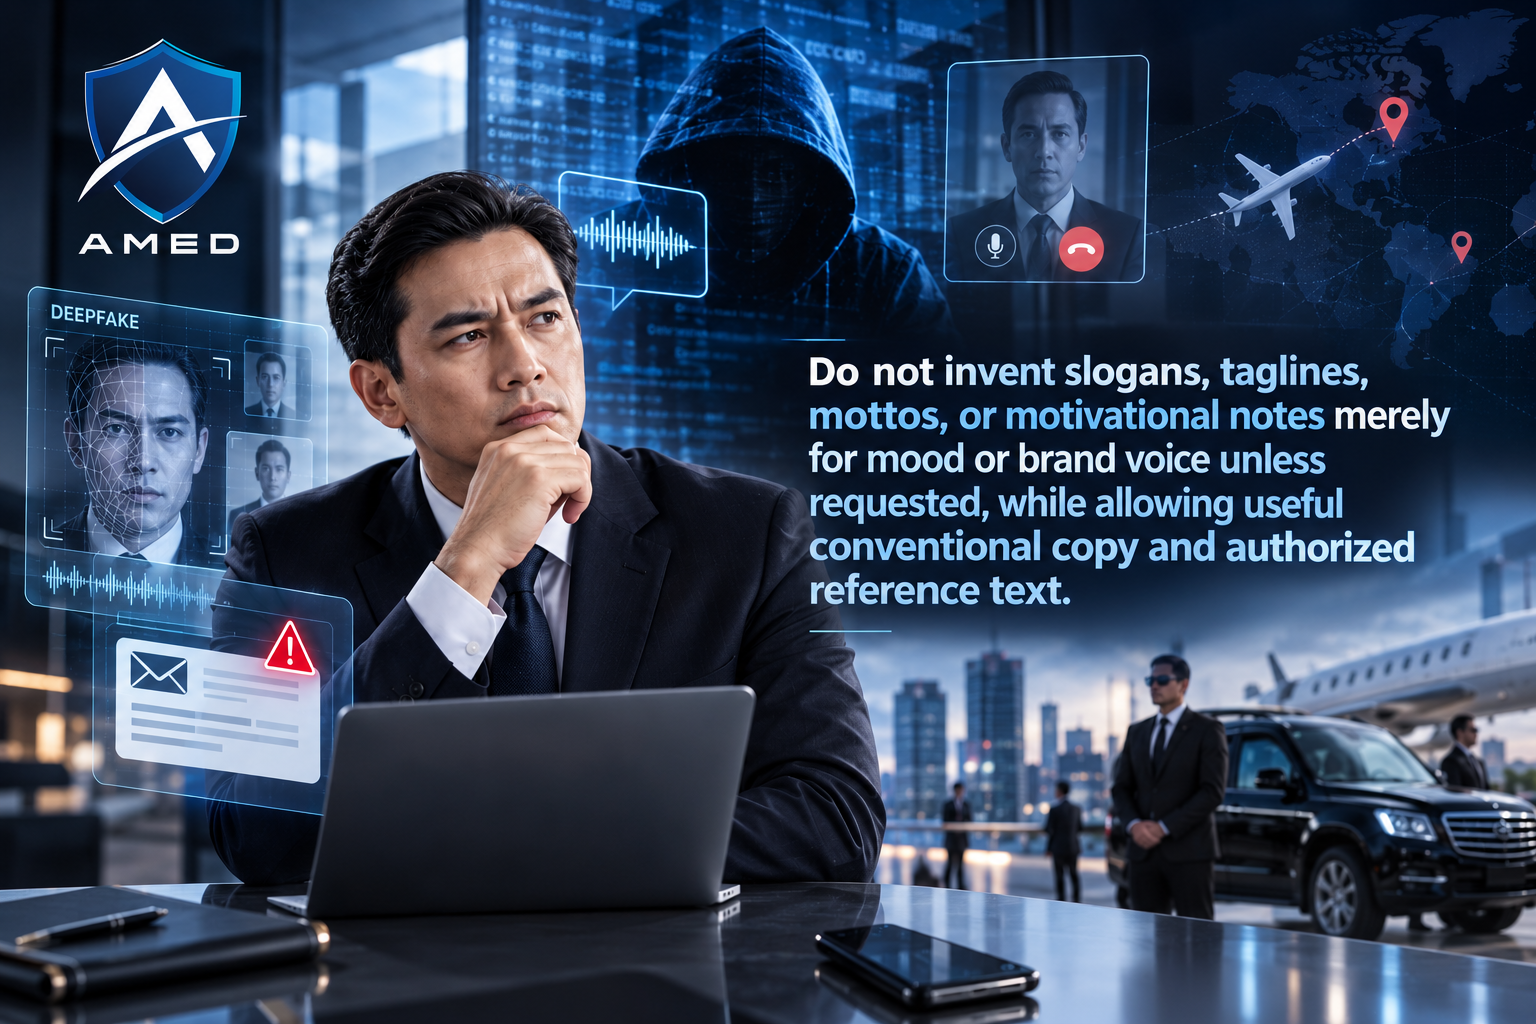
Artificial intelligence is changing more than how companies operate. It is also changing how criminals can research, impersonate, manipulate, and target executives.
For corporate leaders, the risk is increasingly connected across the digital and physical environment.
AI can help attackers create convincing phishing messages, synthetic voices, deepfake videos, falsified documents, and more targeted social-engineering campaigns. The World Economic Forum’s Global Cybersecurity Outlook 2026 reports that 94% of respondents expect AI to be the most significant driver of change in cybersecurity, while 87% identified AI-related vulnerabilities as the fastest-growing cyber risk during 2025.
For organizations, understanding AI security threats executives may face is therefore becoming part of modern executive risk management.
How Is AI Changing Executive Security?
Executives searching for this topic generally want to understand whether AI creates new risks for CEOs, directors, senior managers, VIPs, and other high-profile personnel.
The short answer is yes, but AI is often amplifying existing threats rather than creating entirely new categories of attack.
AI can make reconnaissance faster, phishing more convincing, impersonation more realistic, and social engineering easier to scale. The UK’s National Cyber Security Centre assesses that AI will continue making elements of cyber intrusion more effective and efficient, increasing the frequency and intensity of cyber threats.
For executives, the security model is therefore evolving from:
Physical Protection → Executive Security
toward:
Digital Exposure → Identity Risk → Social Engineering → Travel & Physical Risk → Executive Protection
What Are the Main AI Security Threats Executives Face?
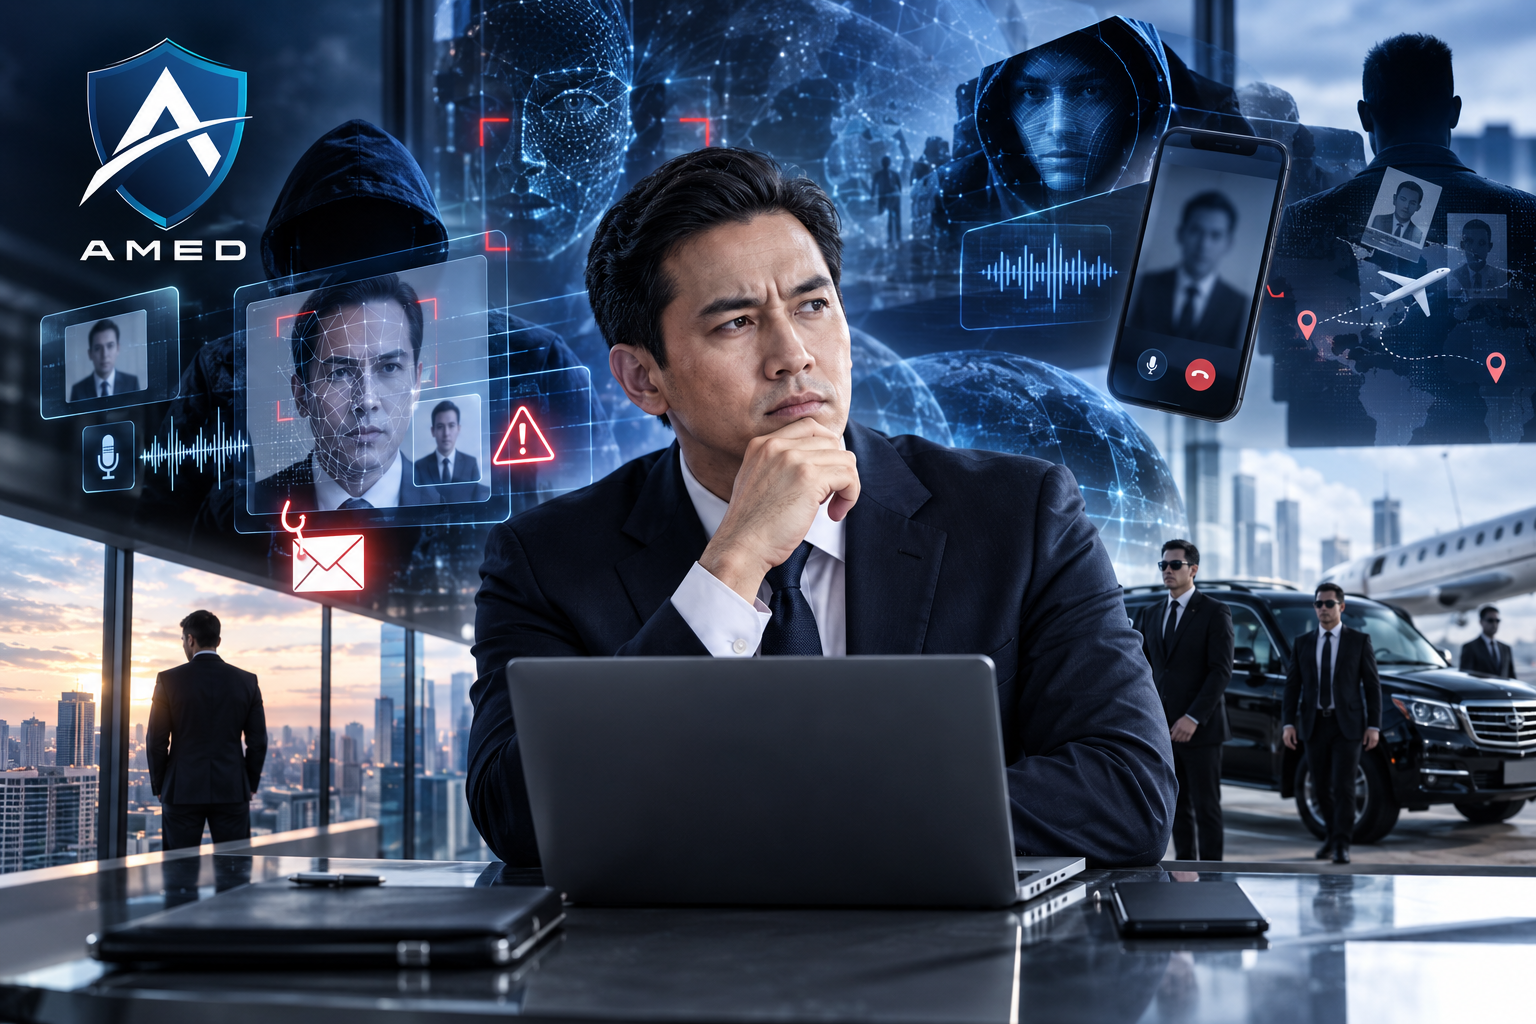
The main AI security threats executives should consider include deepfake impersonation, AI-generated phishing, synthetic voice fraud, targeted social engineering, identity manipulation, automated reconnaissance, data leakage, and AI-assisted cyberattacks.
The World Economic Forum reports that CEOs surveyed for its 2026 outlook ranked cyber-enabled fraud and phishing as their leading cyber concern, while AI-related vulnerabilities ranked second. Among CEOs’ generative-AI concerns, data leaks accounted for 30% and increased adversarial capabilities for 28%.
The implication is important.
An executive security program can no longer consider only:
Where is the executive going?
It should increasingly consider:
Who knows? What information is publicly available? Can the executive’s identity be replicated? Who might trust a fake instruction?
1. Deepfake Impersonation Makes Identity Harder to Trust
One of the most visible AI-related risks is deepfake technology.
AI can generate increasingly convincing synthetic voice, video, and images. This can be exploited to impersonate executives or other trusted individuals.
The NCSC notes that attackers are adopting AI to create deepfake audio and video for impersonation attacks and to produce falsified identity documents capable of defeating weak identity checks.
Imagine a finance employee receiving an urgent video call that appears to come from a senior executive requesting a confidential transfer.
The traditional assumption:
See + Hear = Trust
is becoming weaker.
Organizations increasingly need:
See + Hear + Verify Through Independent Channel = Trust
This is as much a human-security issue as a technical one.
2. AI Makes Phishing and Social Engineering More Convincing
Traditional phishing messages often contained obvious spelling errors, awkward language, or generic messages.
Generative AI reduces those weaknesses.
The World Economic Forum reports that criminals are using generative AI to automate and scale social engineering while producing realistic phishing emails, deepfake audio/video, and falsified documents capable of challenging conventional detection and human scrutiny.
AI can also help criminals customize communication.
Public information from corporate websites, social media, interviews, conference schedules, LinkedIn activity, and other sources can provide context for more personalized approaches.
For executives, this means:
Public Information → AI Analysis → Personalized Message → Impersonation → Social Engineering
The attack may target the executive directly—or an assistant, finance employee, driver, family member, or colleague who trusts the executive’s identity.
3. Executive Digital Exposure Can Become Physical-Security Intelligence
Executive protection traditionally evaluates routes, destinations, meetings, vehicles, schedules, and environments.
Digital exposure adds another dimension.
Public posts may reveal business trips, conferences, hotels, office locations, meetings, vehicles, or recurring routines.
AI can accelerate the analysis of large amounts of publicly accessible information.
The NCSC has assessed that AI provides capability uplift in reconnaissance and social engineering, making both more effective and efficient.
This creates a potential chain:
Digital Footprint → Reconnaissance → Pattern Identification → Targeting → Physical Exposure
Not every online exposure results in a physical threat. However, executive protection planning should increasingly understand how digital information can influence real-world risk.
4. AI-Powered Fraud Is Becoming a Board-Level Issue
AI risk is not limited to cybersecurity teams.
According to the World Economic Forum, 73% of respondents said they or someone in their network had personally experienced cyber-enabled fraud during 2025. CEOs now identify cyber-enabled fraud as their leading cyber concern.
This matters because senior executives often hold authority over financial approvals, confidential information, strategic decisions, and access to other influential people.
Attackers do not necessarily need to compromise the CEO’s computer.
They may instead impersonate the CEO.
That shifts part of the security challenge from:
Protect the Device
to: Protect the Identity + Verify the Instruction + Protect the Individual
5. AI Can Accelerate Reconnaissance Against High-Value Targets
Executives naturally have larger digital footprints than many employees.
Corporate biographies, press releases, social media profiles, public presentations, interviews, event appearances, and company announcements can collectively reveal significant information.
AI makes large-scale information processing easier.
The NCSC expects AI to continue improving threat actors’ ability to perform reconnaissance and social engineering, while its ability to rapidly analyze stolen data can help attackers identify high-value information.
Therefore, modern threat assessment can benefit from considering:
Person → Position → Public Exposure → Digital Footprint → Travel Pattern → Business Context → Threat Scenario
This does not mean executives should disappear from public view.
It means public exposure should become a factor in security planning.
6. Executive Protection Needs a Hybrid Security Mindset
AI does not make traditional executive protection obsolete.
It makes integration more important.
Physical protection remains essential when risk warrants it: secure movement, situational awareness, advance planning, route assessment, protective personnel, and emergency coordination.
However, executive security increasingly needs awareness of digital triggers.
For example:
- Deepfake CEO → Fraud Attempt
- Compromised Schedule → Travel Exposure
- Social Media Intelligence → Location Awareness
- Phishing → Account Compromise → Confidential Information Exposure
- Fake Identity → Manipulation of Staff
The appropriate response is therefore not simply “more bodyguards.”
It is better risk assessment and coordination.
Why AI Security Deserves Executive Attention in 2026
The Global Cybersecurity Outlook 2026 provides several indicators of how quickly this environment is changing.
94% of respondents expect AI to be the biggest driver of cybersecurity change in 2026. 87% identified AI vulnerabilities as the fastest-growing cyber risk during 2025. Meanwhile, the share of organizations assessing the security of their AI tools increased from 37% in 2025 to 64% in 2026.
The UK’s NCSC similarly expects AI to increase the frequency and intensity of cyber threats through 2027, particularly by making parts of intrusion operations more efficient.
In June 2026, Five Eyes cyber agencies also warned that assumptions about cyber risk can become outdated in months rather than years as frontier AI capabilities advance.
The practical lesson for executives is straightforward:
AI Threat Evolution → Continuous Assessment → Updated Protocols → Stronger Resilience
Security planning cannot remain static.
A Business Trip in the AI Era
Consider a fictional CEO traveling to Jakarta for meetings with investors and business partners.
Several days before arrival, public social-media activity reveals the event and approximate schedule.
AI tools could potentially help an attacker aggregate public information about the executive, company, colleagues, and trip.
A targeted phishing message is then sent to the executive’s assistant. Separately, synthetic voice technology is used to imitate an executive requesting a last-minute schedule change.
The security issue now crosses several layers:
Online Intelligence → Impersonation → Staff Manipulation → Schedule Change → Physical Movement
A stronger protocol would independently verify unexpected instructions, restrict unnecessary itinerary exposure, coordinate transportation changes, assess routes, and maintain communication between relevant corporate and protection personnel.
The example demonstrates why cyber awareness and physical security increasingly intersect.
AMED’s Approach to Executive Protection
AMED Corporate Protection & Business Investigation provides executive protection and security-related support for executives operating in Indonesia.
Its published Executive Protection service combines threat assessment, situational awareness, route planning, and executive escort. AMED also provides secure transportation with professional drivers trained in security awareness, route-risk management, airport transfers, and support for business travel.
This operational approach is relevant to emerging AI-related threats because executive security begins with understanding context rather than applying the same protective model to every person.
A modern assessment can consider:
Executive Profile → Digital & Physical Exposure → Destination → Schedule → Threat Assessment → Movement Planning → Protection Measures → Emergency Coordination
AI changes some threat vectors, but the core principle remains the same: identify exposure before determining the appropriate protection.
AMED as Part of the EFBA Business Ecosystem
AMED operates within the broader EFBA Digital Mulia ecosystem, connecting executive-security requirements with a wider business environment.
This relationship is relevant because executives do not operate separately from their organizations.
A security incident can affect:
Executive → Employees → Confidential Information → Operations → Reputation → Business Continuity
Consequently, executive security should be understood as part of broader corporate risk management rather than only personal protection.
For organizations operating in Indonesia, AMED’s approach connects executive protection, secure transportation, business-travel security, and situational awareness with this wider business context.
Internal Links: Build AMED’s Executive Security Topic Cluster
Readers who need personal protection can continue to Executive Protection Indonesia. The service covers threat assessment, situational awareness, route planning, executive escort, secure transportation, and business-travel coordination.
For the wider business perspective, readers can visit EFBA Digital Mulia. Connecting these pages helps establish a logical topic relationship:
Corporate Risk → Executive Security → Secure Transportation → Business Travel → Business Continuity
This structure is also useful for search engines and AI-based discovery systems because each page can answer a specific part of the broader executive-security topic.
FAQ: AI Security Threats Executives
What are the biggest AI security threats executives face?
Major risks include AI-assisted phishing, deepfake voice/video impersonation, identity fraud, automated reconnaissance, targeted social engineering, data leakage, and AI-assisted cyberattacks. The exact risk depends on the executive’s profile, organization, exposure, and operating environment.
Can AI be used to impersonate a CEO?
Yes. AI can generate synthetic audio and video that may be used in impersonation attempts. The NCSC specifically identifies deepfake video and audio as technologies attackers can use for impersonation.
Can AI-related threats create physical-security risks?
Potentially. Digital information may expose travel details, routines, locations, relationships, or schedules that could inform physical targeting. The connection depends on the circumstances and should be evaluated through threat assessment rather than assumed automatically.
Is executive protection only about bodyguards?
No. Professional executive protection can involve threat assessment, situational awareness, advance planning, route management, secure transportation, executive escort, communication, and emergency coordination. AMED’s published service model includes several of these elements.
How should executives respond to deepfake risks?
Organizations can strengthen independent verification procedures for sensitive requests, reduce unnecessary exposure of confidential schedules, strengthen account security, educate key personnel about impersonation, and establish escalation procedures for unusual communications.
Does every executive need close protection?
Security requirements depend on individual risk. Profile, destination, public exposure, travel patterns, business activities, known threats, and local conditions should inform the protection strategy.
How does AMED support executives in Indonesia?
AMED publishes services covering executive protection, secure transportation, and business-travel security, including threat assessment, situational awareness, route planning, executive escort, security-aware drivers, airport transfers, and travel coordination.
Executive Security Must Evolve as Threats Evolve
Artificial intelligence is making it easier to create convincing content, process information rapidly, automate reconnaissance, and manipulate trust.
For executives, that means security can no longer be divided neatly between online risk and physical risk.
A stronger framework is:
Digital Awareness → Threat Assessment → Verification → Situational Awareness → Secure Movement → Executive Protection → Continuous Evaluation
AMED supports executives, VIPs, and corporate personnel requiring professional protection and secure transportation while operating in Indonesia.
Explore AMED Executive Protection
As AI changes the threat landscape, executive protection needs to evolve from simply reacting to incidents toward identifying exposure before it becomes a security problem.